Coordinate multi-client governance without administrative chaos.
Empower your vCISO and security advisory practice with centralized client tenancy, delegated operational workflows, and isolated client governance environments.
| Client Organization | Active Frameworks | Readiness Status | Target Window | Assigned vCISO Lead | Switch Context |
|---|---|---|---|---|---|
AC Acme Cloud Systems Ltd. ACME-09 | SOC 2 T2ISO 27001 | 88% | Q3 Recertification | O. Thakre (Principal Advisory) | |
NK Novak Health Analytics NVK-04 | HIPAAISO 42001 | 74% | Initial Gap Closure | M. Morales (Health Practice) | |
AP Apex Financial Logistics APX-12 | SOC 2 T2PCI-DSS | 94% | Annual Audit Fieldwork | O. Thakre (Principal Advisory) |
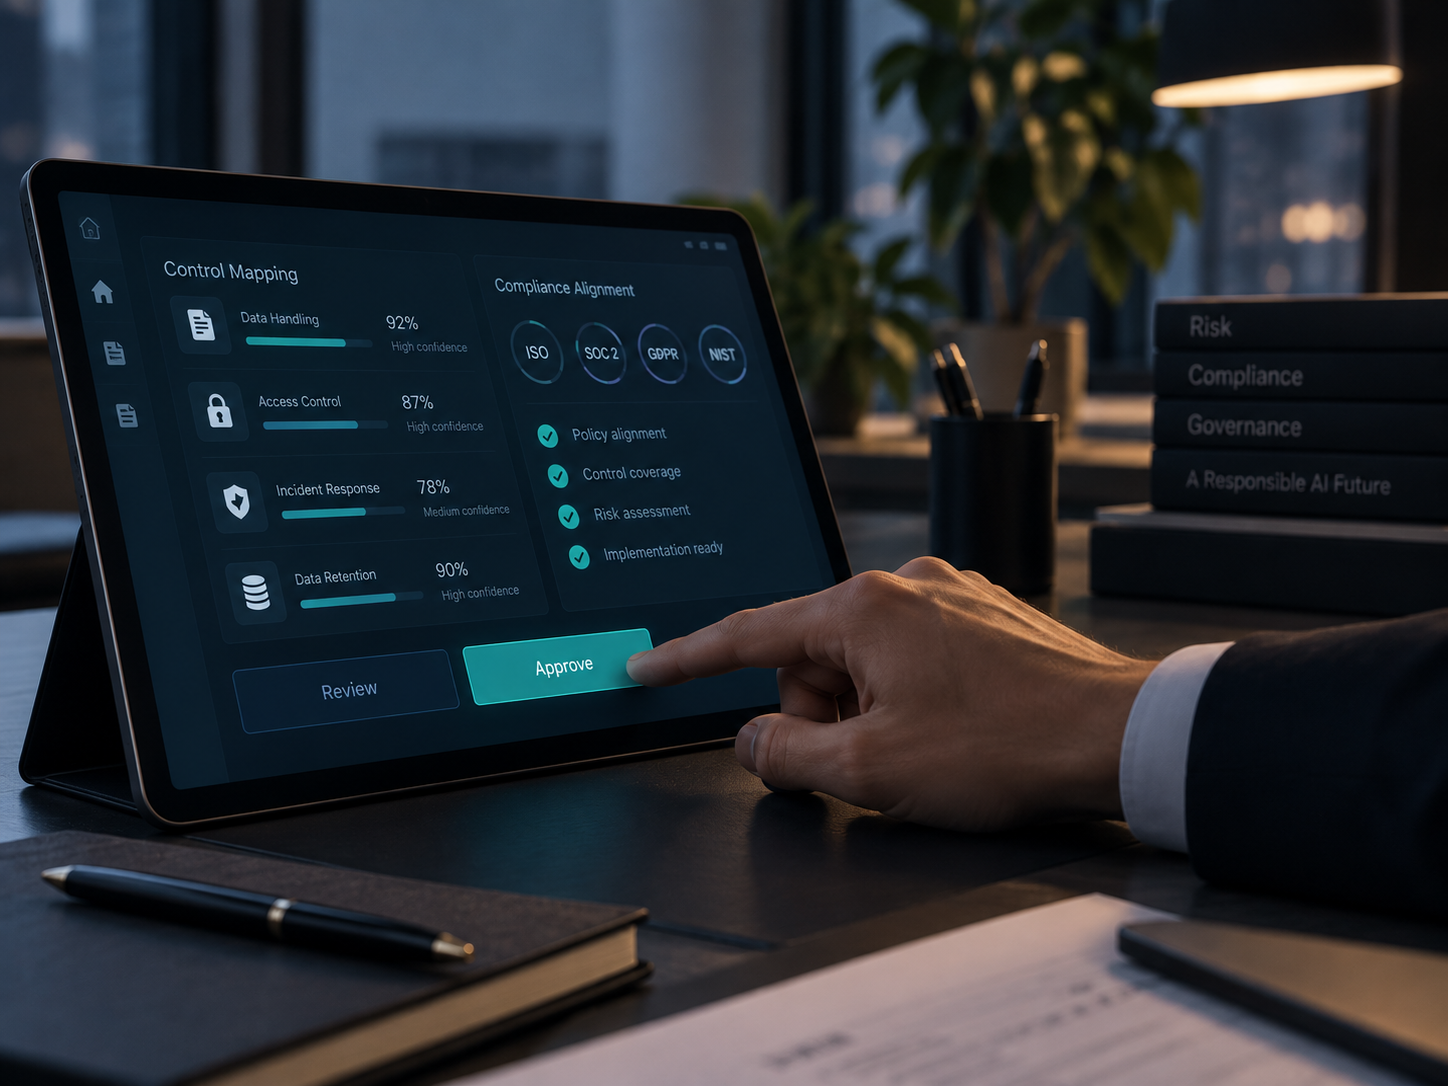
Multi-Client Operations with Isolated Tenant Boundaries
Manage multiple client environments simultaneously while ensuring strict application-level tenant isolation, auditable sign-offs, and client-specific evidence indexing.
Delivering GRC across clients is broken by disconnected workspaces.
Consultants lose billable hours each week maintaining ad-hoc spreadsheets, toggling conflicting client logins, and manually reconstructing the same baseline controls.
Scattered Client Portals & Sheets
Juggling disparate client spreadsheets and tenant credentials introduces data leakage risks, human version errors, and operational drag across advisory staff.
Repetitive Baseline Setup
Re-authoring baseline control standards, audit questions, and compliance cadences from scratch for every newly signed client wastes high-value consulting capacity.
Opaque Multi-Client Status
Lack of a single operational view to assess which client is approaching an audit window, which risks need mitigation review, or which control tests elapsed.
Centralized partner operations with strict organizational isolation.
OMNiGRC structures compliance delivery the way advisory firms operate: top-level partner supervision over clearly separated client organizations.
Client Organization Hierarchy
Provider-level administration managing discrete client organizations with dedicated data boundaries. Ensure lead advisors access authorized client records.
Context Switching
Navigation between client workspaces within authorized partner scopes. Jump directly into a client's risk board or compliance tracker in one click.
Standardized Framework Baselines
Propagate standard control templates across clients while preserving client-specific policies, custom risk scorings, and independent evidence links.
MSSP Provider Console → Client Context Selection → Client Governance Data → Delegated Action & Sign-off
How an advisory team governs a client engagement securely from partner-level oversight down to audit-grade execution.
MSSP Provider Console
Partner leadership reviews aggregate health across client tenants, active audit targets, and global task queues.
Client Context Selection
Select Acme Cloud Systems Ltd.. System establishes application-level tenant isolation parameters.
Client Governance Data
Access client's 5x5 Risk Register, SOC 2/ISO cross-walk, and 90-Day Cadence Board.
Delegated Action & Sign-off
vCISO reviews Advisory AI clause recommendations, assigns corrective owners, and logs defensible audit records.
Core Workflows Purpose-Built for Advisory Practices
Equip your advisory teams with specialized tools needed to deliver high-margin continuous governance.
Compliance Board
Rolling 30/60/90-day task tracking across client accounts. Schedule vendor assessments, policy re-approvals, and access recertifications before they lapse.
Cadence Management →Control Mapping & Crosswalks
Map once across ISO 27001, SOC 2, and GDPR with Advisory AI guidance. Reduce duplicate work when expanding an existing client into subsequent frameworks.
Crosswalk Engine →Business Audit Management
Structured workpapers and mock audits for client audit prep. Package clean digital binders with complete telemetry proof and timestamped approvals for 3rd-party auditors.
Audit Preparation →Risk Register
5x5 Likelihood x Impact scoring tied directly to client-specific technical assets, vendor dependencies, and threat scenarios. Transparent risk treatment plans.
Asset-Centric Risk →Deployment models crafted for regulated partner environments.
Deliver the exact security assurances your most demanding institutional, fintech, or defense-adjacent clients require.
Dedicated Customer-Hosted Instance
Customer controls infrastructure and runtime operations, but receives only Arav-distributed executable artifacts, not the source repository or build/signing infrastructure.
- Infrastructure controlled directly in customer account
- Dedicated environment isolation for high-assurance mandates
- Executable artifacts signed and distributed by Arav
- Audit trail and event log isolation
Managed Multi-Tenant SaaS
Standard secure cloud architecture designed for fast-growing advisory practices and boutique vCISOs who need immediate onboarding without cloud infrastructure overhead.
- Application-level tenant boundary isolation & authorization scopes
- Immediate client tenant provisioning via partner admin console
- Structured application event logging and payload minimization
- Predictable operational scaling for advisory teams
Is OMNiGRC the right partner platform for your advisory practice?
We believe in complete transparency. We built OMNiGRC for disciplined human-led advisory, not autopilot gimmicks.
Ideal Partner Fit
- vCISO & GRC Consultancies: Advisory practices managing recurring security oversight, audits, and governance across multiple client tenants.
- Security Advisory MSSPs: Providers delivering structured continuous compliance monitoring rather than once-a-year audit fire drills.
- Advisory-First Practices: Teams that recognize compliance requires professional human scrutiny and context-aware risk decisioning.
- Multi-Framework Delivery: Practices guiding clients across combined standards like ISO 27001, SOC 2, HIPAA, and ISO 42001.
Not Designed For
- "Click-to-Automate" Magic Compliance Bots: Tools claiming automated audit certifications without human verification or evidence rigor.
- Commodity IT MSPs: Basic desktop support re-sellers without specialized compliance or audit advisory practices.
- Autonomous Auto-Remediation: Systems that alter client production code or infrastructure without explicit administrative approval.
- Single-Checklist Audits: Organizations treating security governance as a static yearly checklist rather than continuous control maintenance.
Elevate your client governance operations.
Deliver structured, auditable GRC advisory services with confidence. Schedule a 1-on-1 walkthrough of the multi-client provider console with our architecture team.